
PaperCut NG/MF Unauthenticated Remote Code Execution

PaperCut NG/MF Unauthenticated RCE
(CVE-2026-81578, CVE-2026-82078)
OVERVIEW
SonicWall Capture Labs threat research team became aware of the threats CVE-2026-81578 and CVE-2026-82078, assessed their impact, and developed mitigation measures. Chained together, these two flaws in PaperCut NG and PaperCut MF, a widely deployed print management platform, give an unauthenticated remote attacker code execution on the Application Server. The first flaw, a Broken Access Control weakness in the web management interface, lets a caller invoke administrative functions with no credentials; the second, an unsafe database-driver class-loading weakness, turns the resulting configuration change into arbitrary code execution. They affect PaperCut NG/MF in all versions before 24.1.10, 25.0.13, and 26.0.5. Classified under CWE-306 (Missing Authentication for Critical Function) and CWE-470 (Use of Externally-Controlled Input to Select Classes or Code), the flaws carry CVSS 4.0 base scores of 8.8 (High) and 9.4 (Critical) respectively (NVD scores them 9.8 and 9.1 under CVSS 3.1). PaperCut published an urgent advisory on August 27, 2026 after detecting active exploitation, with technical analysis contributed by Huntress and watchTowr, and both CVEs were added to the CISA Known Exploited Vulnerabilities catalog on August 31, 2026. Their EPSS scores are 1.62% and 1.69% (75th percentile). Severity is driven by unauthenticated network reach that ends in full code execution. PaperCut NG/MF 24.1.10, 25.0.13, and 26.0.5 remediate both issues, so administrators should upgrade immediately.
TECHNICAL OVERVIEW
PaperCut NG and PaperCut MF are print management servers used across education, government, and enterprise networks. The Application Server exposes a web interface, built on the Apache Tapestry framework, on TCP 9191 by default. Among its features is an external user and card-number lookup that maps card or ID numbers to usernames by running a query against an administrator-configured database. The vulnerable chain reaches that feature without authentication and turns its database configuration into a code-execution primitive.
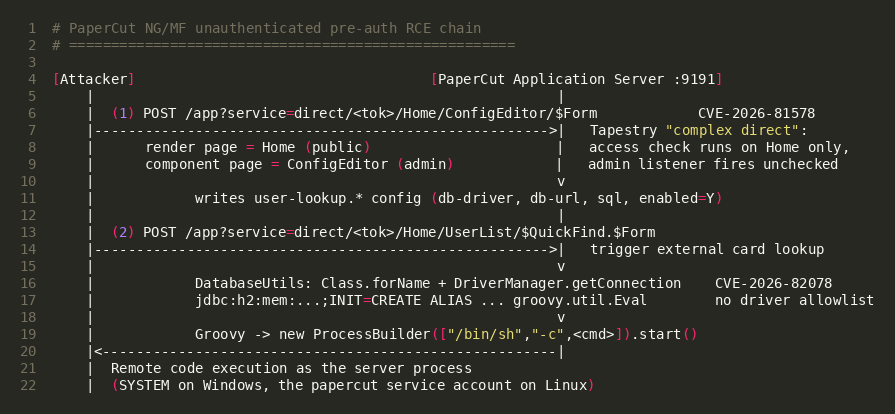
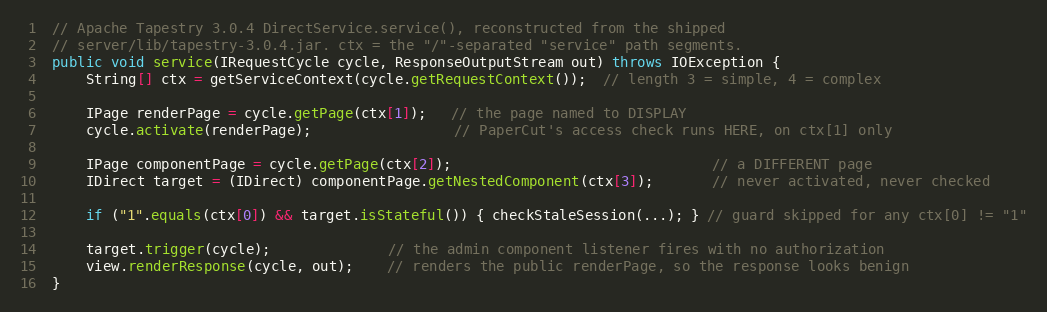
CVE-2026-81578 is the entry point. Tapestry routes requests through a service parameter, and its "complex direct" form names two pages: a page to display and a separate page that owns the component whose listener will run. PaperCut enforces its administrative access check when a page is activated, but the dispatcher activates only the display page. The component page is fetched and its listener is triggered without ever being activated, so no authorization check applies to it. By naming the public Home page for display and an administrative component such as ConfigEditor for execution, an unauthenticated caller invokes privileged functionality while the server renders the innocuous public page in response.
CVE-2026-82078 is the code-execution half. When PaperCut performs an external lookup, its database utilities instantiate the configured JDBC driver by name and open the configured connection URL, with no allowlist constraining either value. Because the attacker controls the driver name, the connection URL, and the lookup SQL through the configuration written in the first step, the connection itself becomes the sink: the bundled H2 database honors an INIT clause in its JDBC URL and runs that SQL as the connection opens, before any query executes.
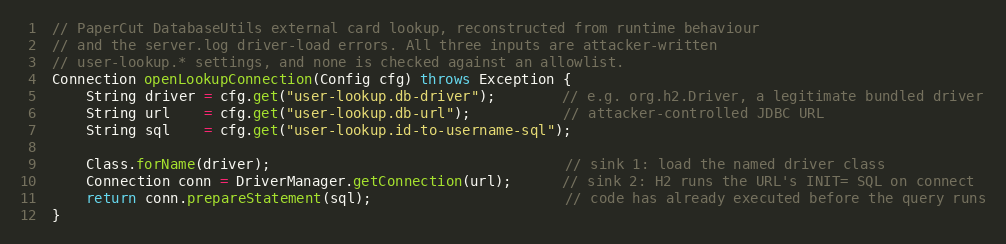
The payload is delivered entirely inside the connection URL. The driver is set to the legitimate bundled org.h2.Driver, and the URL points at an in-memory H2 database whose INIT clause creates a SQL alias for the bundled Groovy evaluator and calls it. The Groovy source constructs a process and runs an operating-system command. No file is written to disk on version 26, because the H2 route executes in memory; versions 24 and 25 reach the same outcome through the bundled Derby engine instead. An allowlist on driver class names would not have stopped this, since the named driver is a genuine PaperCut component and the malicious logic lives in the URL.

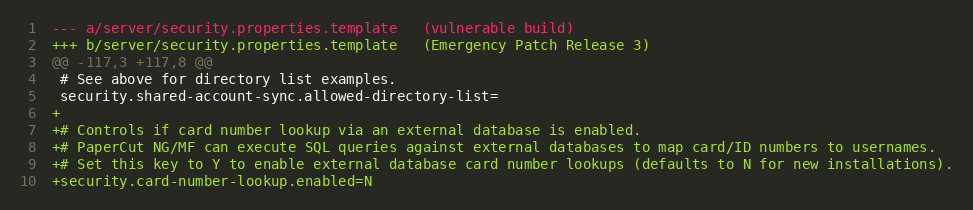
The vendor fix does not attempt to validate the URL. Instead, Emergency Patch Release 3 adds a new security.card-number-lookup.enabled setting that gates the external lookup feature and defaults to off, so the sink is unreachable unless an administrator deliberately turns the feature on. The maintenance releases 24.1.10, 25.0.13, and 26.0.5 carry the same hardening.
TRIGGERING THE VULNERABILITY
The following conditions must be met for successful exploitation of this chain:
- Network-Reachable Application Server: The PaperCut NG/MF Application Server web interface must be reachable over the network. The default listener is plaintext HTTP on TCP 9191, so no interception of TLS is required to observe or deliver the attack.
- Vulnerable Version: The build must be a PaperCut NG/MF release before 24.1.10, 25.0.13, or 26.0.5. Later builds gate the external-lookup sink behind a setting that is disabled by default.
- No Authentication Required: Exploitation needs no credentials. The Tapestry complex-direct request invokes an administrative component through the public Home page, so the access check that guards the administrative interface never runs against the component being triggered.
- Complex-Direct Request Form: The service parameter must use the four-segment complex-direct form, direct/<state>/<renderPage>/<componentPage>/<path>, pairing a public display page with an administrative component page. A legitimate administrator action collapses to the three-segment form where the two pages are the same.
- External Lookup Reachable: The configuration write targets the external card-lookup settings, and the second request triggers a lookup through the user-list quick find. On vulnerable builds the feature path is reachable and executes the attacker-supplied database connection.
EXPLOITATION
Exploiting this chain requires no tooling beyond an HTTP client and no credentials. The attacker sends a short sequence of unauthenticated POST requests to the /app endpoint. The first requests use the complex-direct bypass to drive the administrative ConfigEditor component, writing four external-lookup settings: the JDBC driver is set to the bundled H2 driver, the connection URL is set to an in-memory H2 database carrying an INIT payload, the lookup SQL is set to a harmless placeholder query, and the feature is enabled. A final request drives the UserList quick find with an unmatched value, which makes the server open the configured database connection and, in doing so, execute the INIT payload.

The server answers each request with an ordinary HTTP 200 that renders the public Home page, the same response a benign request produces, so the write and the trigger are not distinguishable from normal traffic in the response body alone. When the connection opens, the H2 INIT clause creates the PCEXEC alias bound to the bundled Groovy evaluator and calls it; the Groovy source launches a process running the attacker's command. The command executes in the context of the PaperCut server process, which is the SYSTEM account on Windows and the service account on Linux.
Video Demonstration
Key Payload Components
| Component | Value | Purpose |
|---|---|---|
| Target Endpoint | POST /app | Tapestry request handler for the Application Server |
| Transport | plaintext HTTP on TCP 9191 | Default web listener, with no TLS unless explicitly configured |
| Bypass Vector | service=direct/<state>/Home/ConfigEditor/... | Four-segment complex-direct form; public display page, admin component |
| Injected Settings | user-lookup.db-driver, db-url, id-to-username-sql, enabled | External-lookup configuration written without authentication |
| Execution Vector | jdbc:h2:mem:...;INIT=CREATE ALIAS ... groovy.util.Eval.me | H2 runs the INIT SQL on connect, invoking the Groovy evaluator |
| Trigger | service=direct/<state>/Home/UserList/$QuickFind.$Form | Opens the poisoned connection through a user-list lookup |
| Execution Primitive | new ProcessBuilder(["/bin/sh","-c",<cmd>]).start() | Runs the operating-system command as the server process |
| Server Response | HTTP 200 rendering the public Home page | A successful attack looks like a benign request |
SONICWALL PROTECTIONS
To ensure SonicWall customers are prepared for any exploitation that may occur due to these vulnerabilities, the following signatures have been released:
| Signature ID | Signature Name |
|---|---|
| IPS: 22435 | PaperCut NG/MF Broken Access Control (CVE-2026-81578) |
| IPS: 22436 | PaperCut NG/MF Configuration Injection (CVE-2026-82078) |
REMEDIATION RECOMMENDATIONS
The risks posed by CVE-2026-81578 and CVE-2026-82078 can be mitigated or eliminated with the following measures:
- Upgrade PaperCut NG/MF: Move to 24.1.10, 25.0.13, or 26.0.5 or later, where the external card-lookup feature is gated behind a setting that is disabled by default. This is the direct fix and should be applied to every Application Server, including site and secondary servers.
- Restrict Network Exposure: The Application Server web interface should not be reachable from the public internet. Firewall TCP 9191, along with the HTTPS ports, so the interface is reachable only from trusted administrative networks.
- Leave External Card Lookup Disabled: On patched builds, do not enable security.card-number-lookup.enabled unless the external database lookup is genuinely required, since that setting is what re-exposes the class-loading sink.
- Monitor for Exploitation Artifacts: Inspect the PaperCut server log for external-lookup errors that indicate a poisoned connection, such as DatabaseUtils card-lookup entries referencing jdbc:h2:mem, VALUES CAST, or a missing driver, and alert on unexpected child processes spawned by the server or outbound connections from the host shortly after such entries.
- Deploy IPS Signatures: Apply the signature coverage above at the perimeter and on any segment that can reach the Application Server, and keep signature sets current.
- Segment the Network: Isolate application servers from sensitive internal resources and implement egress filtering to detect unauthorized outbound connections.
RELEVANT LINKS
- PaperCut Urgent Security Advisory (27 August 2026)
- National Vulnerability Database (NVD): CVE-2026-81578
- National Vulnerability Database (NVD): CVE-2026-82078
- CISA Known Exploited Vulnerabilities Catalog
- CWE-306: Missing Authentication for Critical Function
- CWE-470: Use of Externally-Controlled Input to Select Classes or Code
- EPSS API: CVE-2026-82078
- PaperCut NG/MF Download and Release History
ATTRIBUTION
CVE-2026-81578 and CVE-2026-82078 were disclosed by PaperCut Software in an urgent security advisory on August 27, 2026, after the company identified active exploitation in the wild. Huntress and watchTowr contributed technical analysis that informed the emergency patches, and fixes shipped in PaperCut NG/MF 24.1.10, 25.0.13, and 26.0.5.
Third-party vulnerability database mirrors:
- GitHub Advisory Database: github.com/advisories/GHSA-mjg5-wj9r-9mfx
- Rapid7 Metasploit Framework: github.com/rapid7/metasploit-framework/pull/21842
Share This Article

An Article By
An Article By
Security News
Security News
