
Hidden in Plain Sight: Closing the Encrypted Traffic Blind Spot with Cloud Secure Edge
by Amelia Foss

Closing the Encrypted Traffic Blind Spot with Cloud Secure Edge
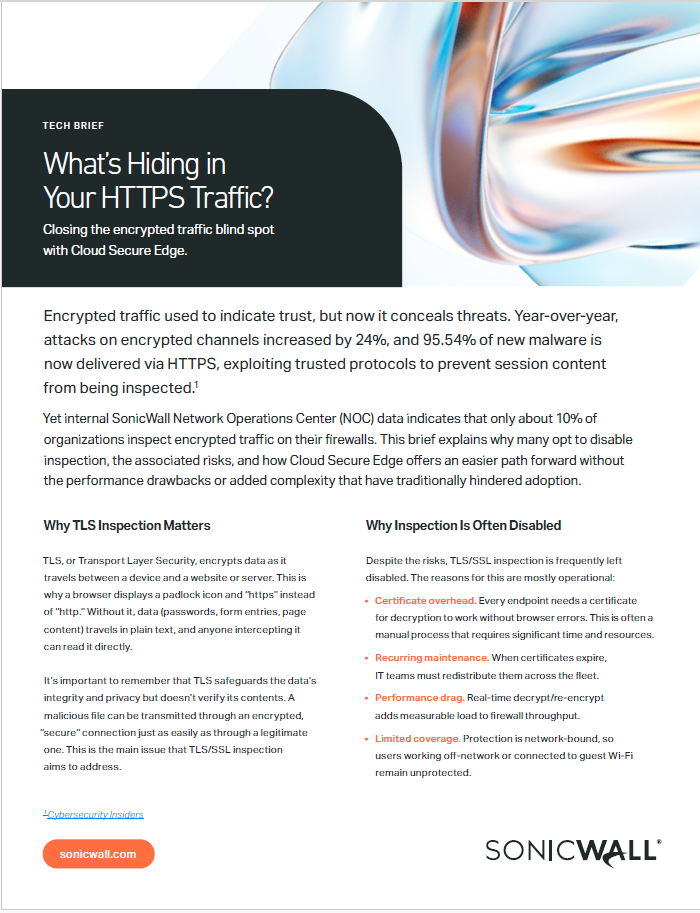
What was once a trust signal for secure traffic has become a hiding place for threats. Recent studies show that attacks using encrypted traffic rose 24% year-over-year, with 95.54% of all new malware now delivered via HTTPS, often routed through trusted platforms to evade scrutiny. Attackers exploit this gap because firewalls and other perimeter defenses cannot see what is transmitted inside an encrypted session unless they are specifically configured to decrypt and inspect it.[1]
Yet, despite being one of the most powerful attack-prevention controls available, adoption of traffic inspection remains low. This article examines why so few organizations enable TLS/SSL inspection, its associated risks, and how Cloud Secure Edge offers a simplified path to protection without the performance and complexity of trade-offs that have historically limited its adoption.
What Is TLS/SSL Inspection, and Why Does It Matter?
TLS (Transport Layer Security) encrypts most web traffic, ensuring data integrity during transmission between a device and a website or server. This is why browsers display a padlock icon and use “https” instead of “http.” Without TLS, sensitive data such as passwords, form entries, and page content is transmitted in plain text, meaning it would be easily read and exploited if the traffic is intercepted. Yet, while TLS protects data integrity and privacy, it does not verify the safety of the content. As a result, encryption can prevent firewalls that analyze only packet headers from detecting malicious activity, allowing malware to pass through trusted traffic. Additionally, attackers often obtain legitimate certificates for malicious domains, so HTTPS with a padlock icon does not guarantee security.[2]
TLS/SSL inspection addresses this vulnerability by decrypting, inspecting, and re-encrypting the session, sending it along to its destination only if no threats or vulnerabilities are found.
Why TLS/SSL Inspection Rarely Gets Activated
Today, over 90% of internet traffic is now TLS-encrypted, creating a vast blind spot for firewalls without inspection enabled. However, like any security measure, inspection is only effective when used correctly - or at all. When a control causes operational complexity, disrupts users, degrades performance, or leaves coverage gaps, people tend to avoid it.
- Certificate overhead. Enabling inspection requires generating or downloading a certificate, which IT must then distribute to every endpoint before traffic can be decrypted without triggering browser errors. This is often a manual process that requires significant time and resources.
- Ongoing maintenance. When that certificate expires, the entire distribution process must be repeated across every device, creating a recurring administrative burden.
- Performance impact. Decrypting and re-encrypting traffic in real time places additional load on the firewall, which can create a measurable drag on throughput, particularly on higher-volume networks.
- Limited coverage. Because this protection is network-bound, it only applies to traffic passing through the firewall. Users working off-network or connected to guest Wi-Fi remain unprotected.
For most IT teams, the ongoing effort required to keep TLS/SSL inspection running outweighs the perceived benefit of turning it on in the first place.
How Cloud Secure Edge Closes the Gap
SonicWall Cloud Secure Edge is a cloud-delivered Security Service Edge (SSE) solution that provides zero-trust access to corporate resources and real-time internet security for every user and device, wherever they connect. The Secure Internet Access license builds on standard TLS inspection by removing its operational overhead and extending protection to users everywhere, not just those inside the corporate network.
- Follows the user, not the network. Because CSE is cloud-delivered rather than tied to a single firewall, inspection applies whether someone is on the corporate network, working remotely, or connected to guest Wi-Fi, closing the off-network gap.
- No manual certificate distribution. Authentication tokens and certificates renew automatically in the background, so users are not dropped to a registration screen or prompted to re-enroll when a token renews.
- Minimal re-enrollment. Re-enrollment is only required after long periods of inactivity, replacing the recurring, device-by-device redistribution that traditional TLS inspection requires.
- Higher inspection capacity. File analysis runs at a 100MB limit, compared to 10MB on the firewall, allowing deeper malware analysis.
- Scales with the workforce. Protection extends to every user and device without adding appliance-level throughput strain.
The Long-Term Payoff of TLS Inspection with Cloud Secure Edge
Closing the encrypted traffic gap does more than reduce risk. It changes what security teams can reasonably expect to deliver - and at what cost - once decryption no longer requires a trade-off between protection and performance.
- Reduced risk of breach. With the majority of malware now delivered over HTTPS, enabling inspection directly addresses the channel attackers rely on most, rather than leaving it as an accepted blind spot.
- Lower IT overhead. Removing manual certificate management and re-enrollment frees security teams from a recurring administrative task, allowing them to focus on higher-value work.
- Consistent protection across a distributed workforce. As remote and hybrid work remain the norm, protection that follows the user rather than the network closes a coverage gap that traditional, appliance-bound inspection cannot.
- Stronger compliance posture. Consistent visibility into encrypted traffic supports data protection and regulatory requirements that depend on demonstrable monitoring and control of sensitive information in transit.
- Scalability without added infrastructure cost. Because inspection is cloud-delivered, organizations gain expanded protection without the appliance upgrades or throughput trade-offs typically required to scale firewall-based inspection.
Getting Started
TLS inspection is included in Cloud Secure Edge's Secure Internet Access Advanced, giving organizations a way to close the encrypted traffic gap without the certificate overhead, throughput trade-offs, or network limitations that have kept this control out of reach for most.
Learn more about Secure Internet Access: https://www.sonicwall.com/products/secure-internet-access
Learn More on This Topic
WEBINAR
HTTPS Inspection Without the Headaches: Closing the Encrypted Traffic Blind Spot
Join us live or on-demand: Oct 8, 2026, at 10 AM PST/1 PM ESTTECH BRIEF
Sources: [1] Cybersecurity Insiders | [2] SecurityScorecard
Share This Article

An Article By
An Article By
Amelia Foss
Product Marketing Specialist
Amelia Foss
Product Marketing Specialist