
DarkKomet Trojan resurfaces in the wild (May 17, 2013)

The Dell SonicWALL Threats Research team has received reports of a Delphi based backdoor Trojan. This Trojan appears to be a version of the DarkKomet Remote Administration Tool (RAT).
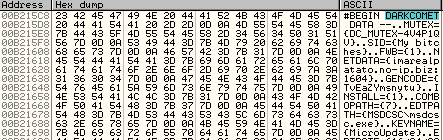
Infection Cycle:
Upon execution The Trojan makes the following DNS query, although at the time of analysis this URL is offline:
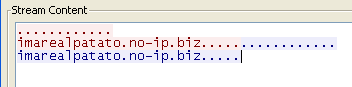
It then drops the following file on the system:
- %USERPROFILE%My DocumentsMSDCSCmsdcsc.exe (a copy of itself)
In order to start after reboot the Trojan adds the following keys to the registry:
- HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun MicroUpdate "%USERPROFILE%My DocumentsMSDCSCmsdcsc.exe"
- HKEY_LOCAL_MACHINESOFTWAREMicrosoftWindows NTCurrentVersionWinlogon " Userinit "C:WINDOWSsystem32userinit.exe, %USERPROFILE%My DocumentsMSDCSCmsdcsc.exe"
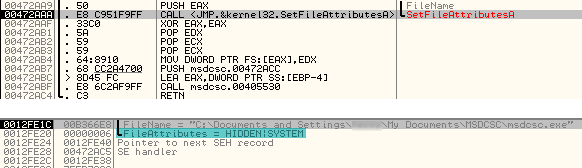
It then changes the file's attributes to hide it:
The Trojan monitors the keyboard and records all the actions to a file:
- %APPDATA%dclogs.dc
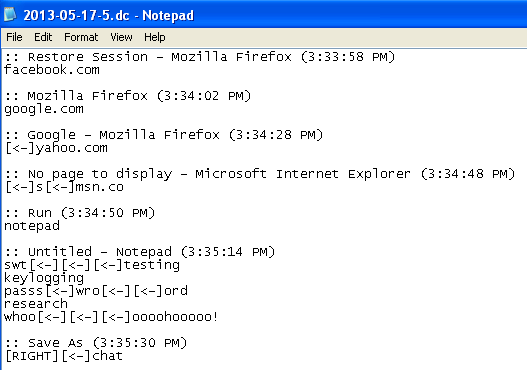
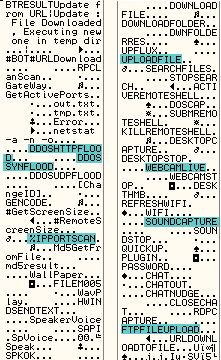
Apart from the keylogging functionality, further analysis reveals additional features such as administering DDoS attacks, sound capture, executing and uploading files and controlling your webcam.
Dell SonicWALL Gateway AntiVirus provides protection against this threat with the following signature:
- GAV: DarkKomet.A_2 (Trojan)
Share This Article

An Article By
An Article By
Security News
Security News
